Aleksi Suhonen – Automating DNS Secondaries with Catalog Zones
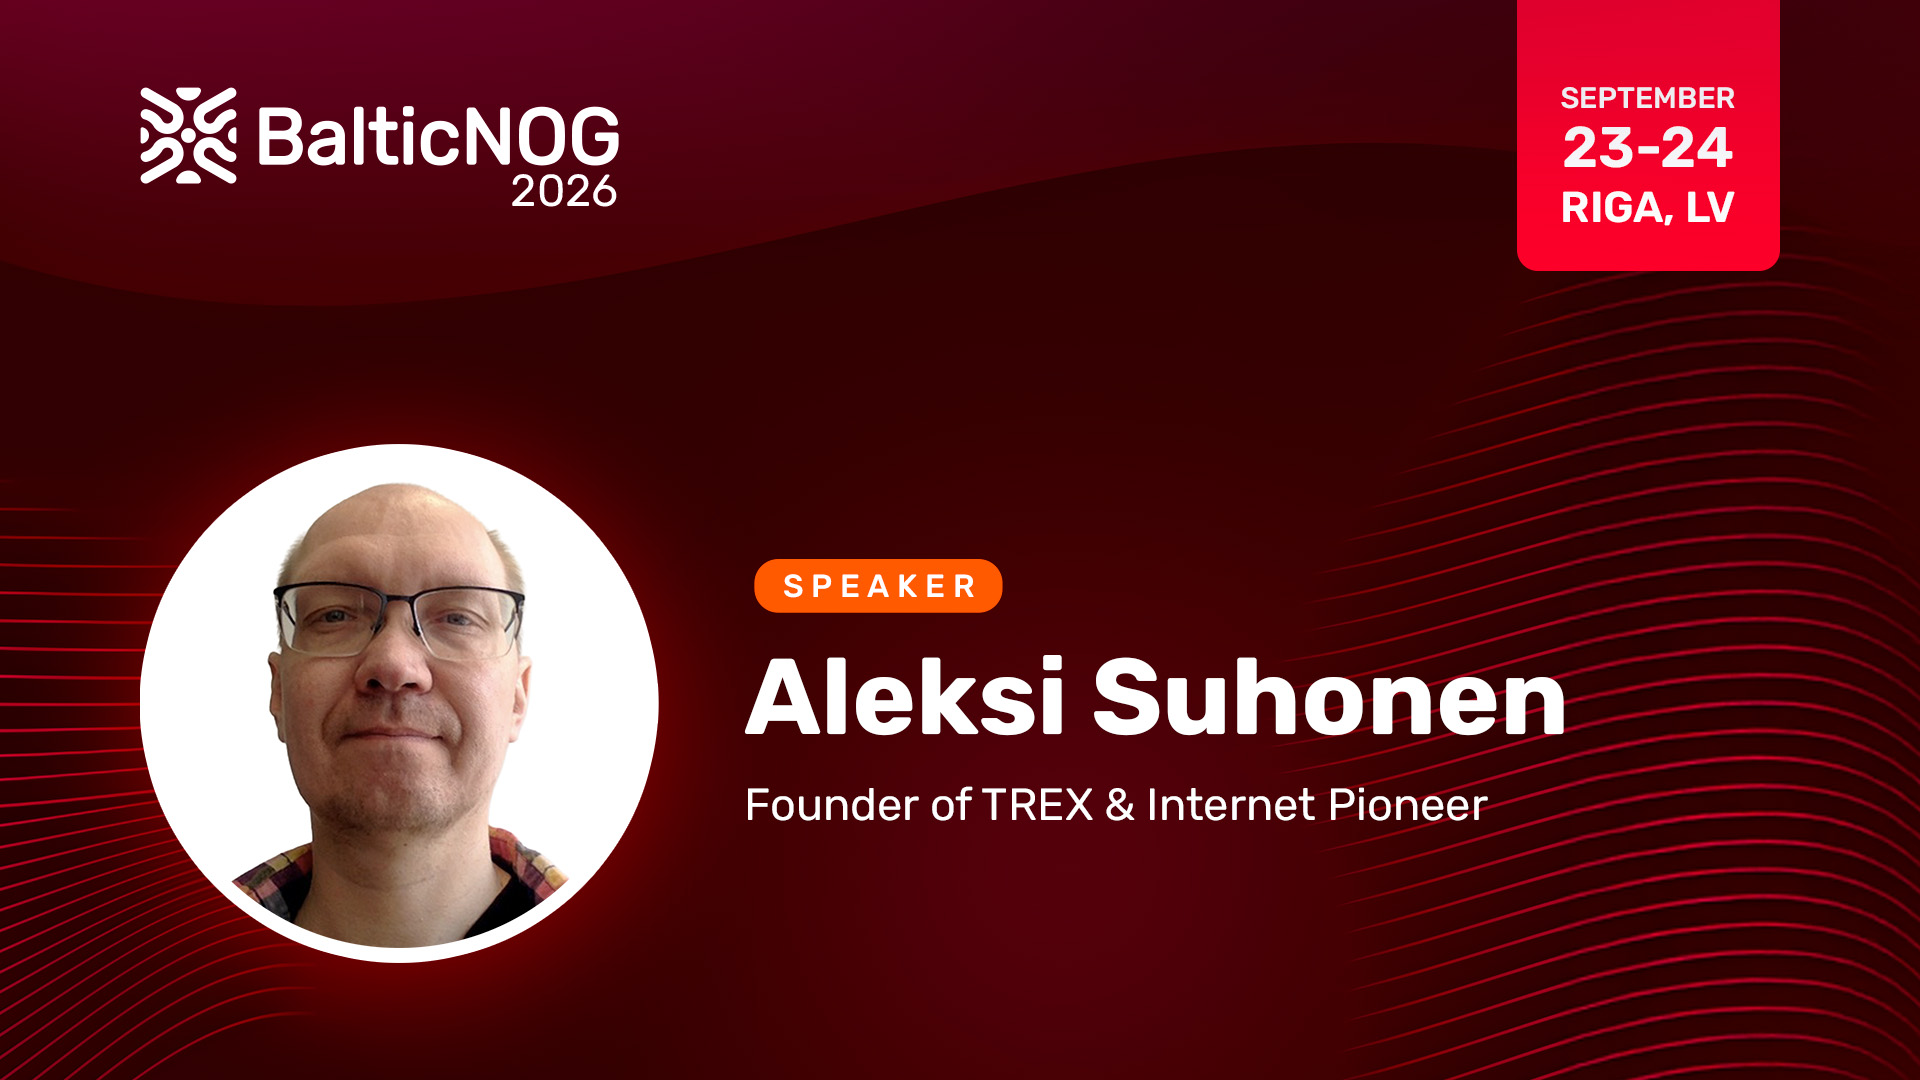
Aleksi Suhonen first got on the internet in 1987. He started working with ISPs and IXPs in 1997 and founded TREX in 2002. He began studying Computer Engineering and Software Engineering at Tampere University of Technology in 1994, but work pulled him away the following year. He worked on network maintenance and security at the university and later at Nokia Mobile Phones. By 1997 he had moved to SciFi Communications International, which later became known as Saunalahti and Jippii, where he led the international network expansion of AS6667, connecting it to half a dozen IXPs across Europe and the United States.
At BalticNOG 2026, Aleksi will bring this background to the stage with his talk, “Automating DNS Secondaries with Catalog Zones.”
The Problem With Keeping DNS Servers in Sync
Running DNS servers across diverse, redundant connections only works if every server agrees on the same list of zones and zone contents. Aleksi’s talk starts with this synchronization problem and why it’s harder than it sounds once a network grows beyond a handful of servers. Many existing approaches solve it by reaching outside DNS entirely, adding another system to configure, secure, and keep in sync with the DNS servers themselves.
Doing It All in DNS
Catalog Zones, defined in RFC 9432, take a different approach: they handle zone provisioning entirely in-band, using DNS itself as the transport. A producer distributes a catalog, which is just a regular DNS zone listing which zones should exist, to consumers who then provision themselves accordingly. Producers aren’t necessarily primaries, and consumers can be either primaries or secondaries, which makes the mechanism flexible enough to fit into different network designs.
Aleksi will walk through how this works in practice, including how consumers pick up group-level configuration alongside the catalog itself, and how newer proposals extend the mechanism to signal things like which primary to transfer from, which TSIG keys to use, and other access control details, directly within the catalog zone. He’s hosted hackathons on this exact topic before, and plans to adapt some of that material into the talk.
Why You Shouldn’t Miss This Talk
If you run DNS infrastructure across more than one server, you’ve dealt with some version of the synchronization problem this talk addresses. Catalog Zones offer a way to solve it without adding another system outside DNS to manage, and Aleksi’s talk gives you a clear picture of how the mechanism actually works.
Whether you run authoritative DNS today or are evaluating how to scale a diversely connected setup, this talk gives you a grounded look at a mechanism worth understanding.
📅 When: 23-24 September 2026
📍 Where: BalticNOG 2026, Riga, Latvia
🔗 Don’t miss BalticNOG! Register today: https://balticnog.org/tickets/